Website · Open source · 2026
Bounty Atlas
A searchable research atlas for building an autonomous bug-bounty agent: 1,216 catalogued sources, 15 papers, 36 reference repositories and an OWASP-based taxonomy.
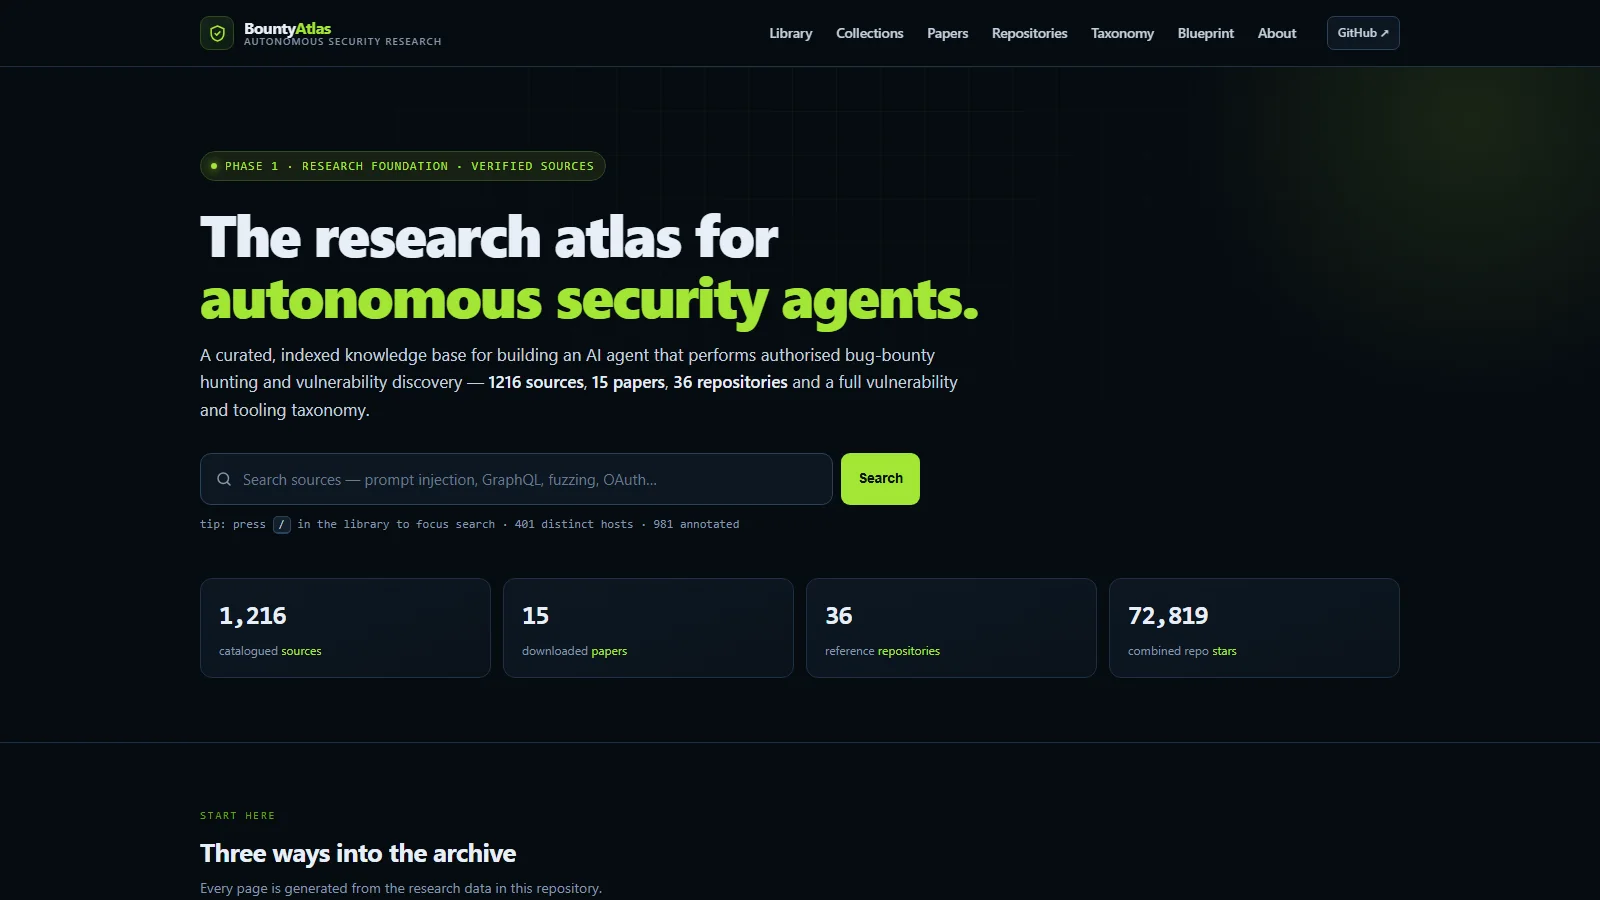
- 1,216
- catalogued sources
- 15
- papers, downloaded and indexed
- 36
- reference repositories
Building an agent that hunts vulnerabilities starts with a reading list nobody has time to assemble. This project collects the methodology, papers, tooling and real-world patterns into one place, then publishes them as a site you can search instead of a folder of markdown.
What we built
- A catalogue of 1,216 unique sources across 401 hosts, each with a collection, a description and an annotation
- 15 papers downloaded and indexed, and 36 reference repositories with 72,819 stars between them
- A vulnerability taxonomy from the OWASP classes plus 22 further classes, and a tooling map of 20 groups
- Client-side search over titles, descriptions and hosts, with collection filters, four sort orders and shareable URLs
- A site generated from the research files on every build, so a new source is added in one place and the catalogue stays authoritative
The scope is broad on purpose: web, APIs, cloud, containers, mobile, wireless, Web3, memory corruption, supply chain, LLM security and agent security. Sources are catalogued, not endorsed. The phase this covers is research and curation; it is a knowledge base for authorised testing, not a scanner.